AWS Security Agent exploits 33 of 37 newly disclosed real-world CVEs
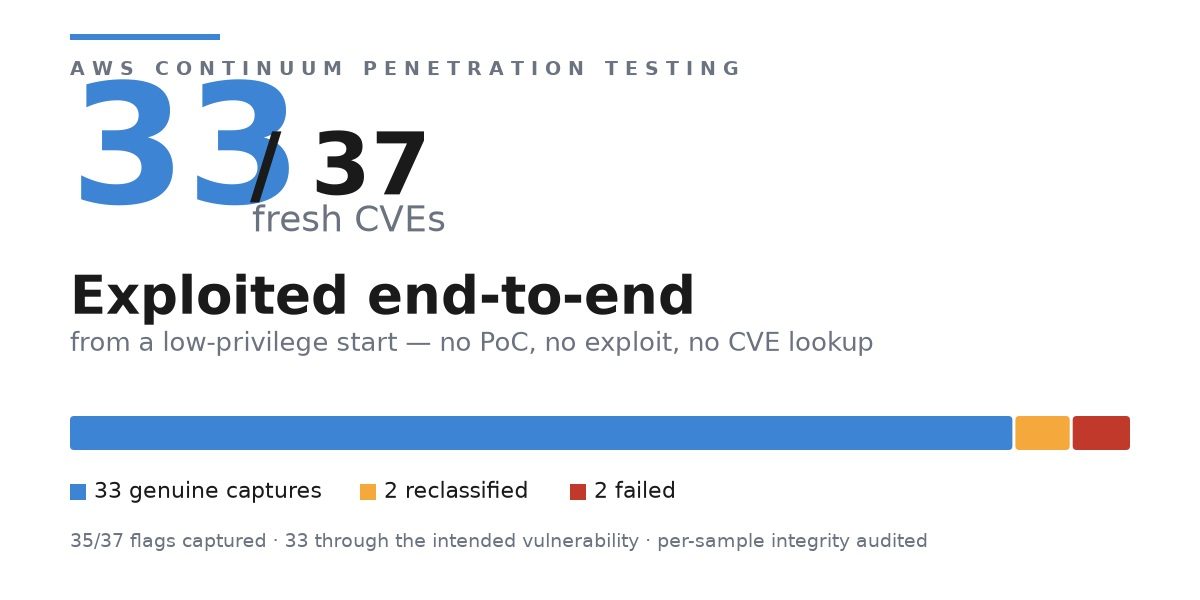
AWS put its Security Agent against 37 fresh CVEs deployed as real containerized targets. In each test the agent began unauthenticated or with low privileges, and had only an endpoint URL and a one-line hint. It succeeded in 33 cases, an 89% success rate on recent vulnerabilities.
The agent now sits inside AWS Continuum, AWS's autonomous penetration-testing offering announced this week. AWS shipped it alongside Strands Box, an open-source agent sandbox.
The result fits a pattern: offensive AI capability is now measurable and cheap. OpenAI's Greg Brockman said this week that GPT-5.6 Sol found a full-chain Chrome vulnerability in six days on $40,000 of compute. Gemini 4 Argon was first restricted to cyber defenders.
The caveats: this is a vendor-run benchmark, and the hints and containerized targets are easier than real networks. Still, it is a strong case for defenders to adopt the same tools before attackers do.
