Strands agents CVE-2026-18394: model-chosen proxy parameter leaked credentials
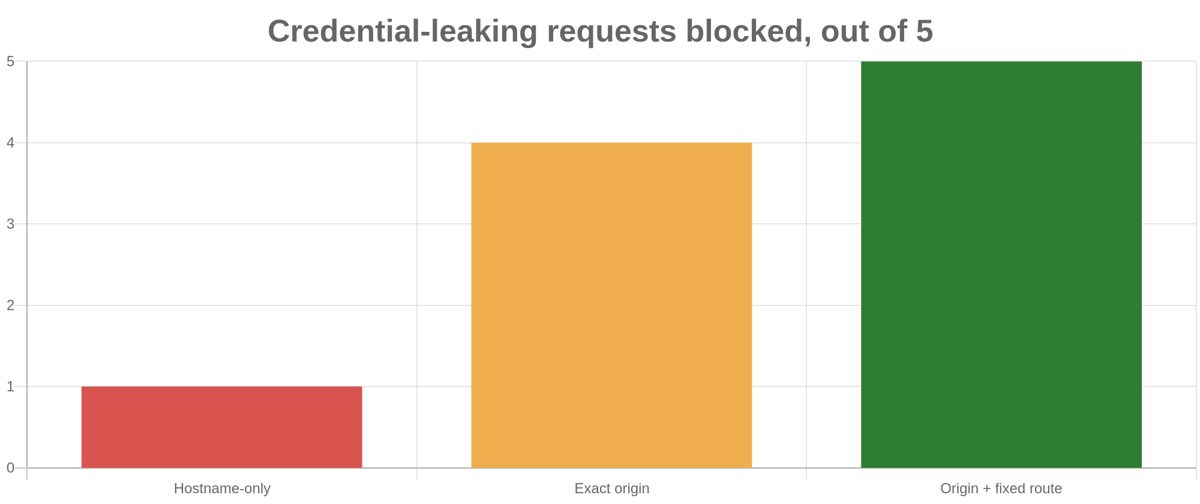
AWS disclosed CVE-2026-18394 in bulletin 2026-069-AWS. The flaw sits in the http_request tool of strands-agents-tools, part of AWS's open-source Strands agent framework. The tool scoped credentials to approved hostnames, a common pattern meant to stop an agent from sending secrets to arbitrary servers. But the model itself could choose a proxies argument.
The attack path follows from that. Prompt-injected content, such as a malicious web page or document, could instruct the agent to send an otherwise legitimate request to an allowlisted host through an attacker's proxy. The credentials would then pass through infrastructure the attacker controls. The dev.to write-up sums it up: "the allowlist guarded the destination, not the route." Any tool parameter a model can set is part of the attack surface, not just the URL.
The disclosure lands in a week dominated by agent-safety infrastructure. AWS shipped Nitro Sandboxes for isolating agent code, NVIDIA's agentic stack includes an OpenShell sandbox designed to keep credentials out of an agent's reach, and Bedrock AgentCore is now used by tens of thousands of customers. The Strands bug shows that sandboxing compute does not address credential exfiltration through tool arguments.
Teams running Strands should upgrade the tools package and audit any custom tools that expose networking options to the model. The broader lesson for agent builders is to treat every model-controllable parameter as untrusted input.